Spring Security 整合 thymeleaf 实现动态权限 (2)项目基本配置
文章目录
项目基本配置
创建一个基本的springboot项目。基本依赖如下
    <!-- thymeleaf模板-->
        <dependency>
            <groupId>org.springframework.boot</groupId>
            <artifactId>spring-boot-starter-thymeleaf</artifactId>
        </dependency>
        <!-- springweb-->
        <dependency>
            <groupId>org.springframework.boot</groupId>
            <artifactId>spring-boot-starter-web</artifactId>
        </dependency>
        <!-- spring security-->
        <dependency>
            <groupId>org.springframework.boot</groupId>
            <artifactId>spring-boot-starter-security</artifactId>
        </dependency>
        <!-- SpringBoot集成mybatis框架 -->
        <dependency>
            <groupId>org.mybatis.spring.boot</groupId>
            <artifactId>mybatis-spring-boot-starter</artifactId>
            <version>${mybatis.spring.boot.starter.version}</version>
        </dependency>
        <!-- mysql驱动-->
        <dependency>
            <groupId>mysql</groupId>
            <artifactId>mysql-connector-java</artifactId>
            <scope>runtime</scope>
        </dependency>
application.yml配置
spring:
  datasource:
    driver-class-name: com.mysql.cj.jdbc.Driver
    url: jdbc:mysql://localhost:3306/security?serverTimezone=UTC&useUnicode=true&characterEncoding=utf-8&useSSL=true
    username: root
    password: 你的数据库密码
  thymeleaf:
    #是否缓存
    cache: false
    # 在构建URL时预先查看名称的前缀
    prefix: classpath:/templates/
    # 构建URL时附加查看名称的后缀
    suffix: .html
  #mybatis配置
mybatis:
  mapper-locations: classpath:mapper/*.xml
创建实体类以及基本的mapper,这里使用easycode自动生成。
并对User实体类进行相应的改造,
/**
 * 系统用户(User)实体类
 *
 * @author sdl
 * @since 2020-03-22 15:15:14
 */
public class User implements UserDetails, Serializable {
    private static final long serialVersionUID = -52166883900608909L;
    /**
    * ID
    */
    private Integer id;
    /**
    * 用户名
    */
    private String username;
    /**
    * 密码
    */
    private String password;

    其他属性省略...
    Getter and Setter省略...
    private List<Role> roles;

   //UserDetails的角色资源属性集合
    @Override
    public Collection<? extends GrantedAuthority> getAuthorities() {
        List<SimpleGrantedAuthority> authorities = new ArrayList<>(roles.size());
        for (Role role : roles) {
            authorities.add(new SimpleGrantedAuthority(role.getName()));
        }
        return authorities;
    }
   // 账号是否未过期
    @Override
    public boolean isAccountNonExpired() {
        return true;
    }
    // 账号是否未锁定
    @Override
    public boolean isAccountNonLocked() {
        return true;
    }
    // 账号凭证是否未过期
    @Override
    public boolean isCredentialsNonExpired() {
        return true;
    }
    // 账号是否可用,数据库中定义了enabled字段
    @Override
    public boolean isEnabled() {
        return enabled;
    }
以及相应的dao层方法和mapper
dao

mapper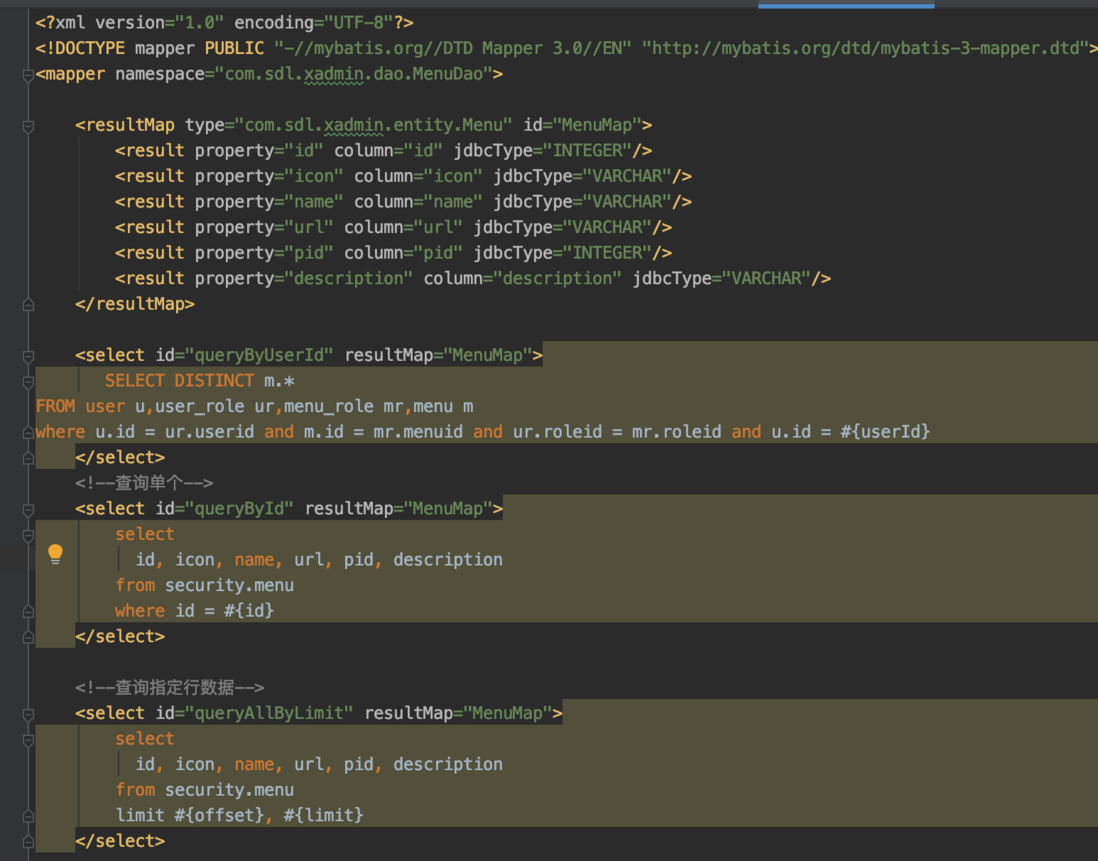
评论
登录后参与技术讨论,分享你的经验与见解。
登录 / 注册暂无评论