国外登录太坑了,都是一点点总结到这里做个记录。服务端验证登录国外登录的前提是有一台服务器在国外或者配置国外服务器代理,此方直接代理到香港服务器请求。
目前收到几个google, facebook, twitter, line~~~~服务端登录,不提现客户端实现。简要的贴部分PHP代码参考,其他语言互通
- 首先客户端授权获取idToken,服务端得到这个授权后直接请求google进行验证
- 请求https://oauth2.googleapis.com...{idToken}
- 得到用户的信息进行自己业务的操作
- 参考:https://developers.google.com...
- 首先是客户端授权获取得到accessToken、faceBookId
- 请求https://graph.facebook.com/{faceBookId}?access_token={access_token}&fields=id,picture,name"
- 得到用户信息和客户端的faceBookId进行对比
- 进行自己业务
- 参考:https://blog.csdn.net/mycwq/a... 里面的请求地址需要注意
- 客户端获取到idToken【客户端返回:rawString】
- POST请求 https://api.line.me/oauth2/v2...{idToken}&client_id={clientId}
- 操作返回的数据,实际就是验证idToken的有效性
- 参考:https://developers.line.biz/e...
- twitter就比较麻烦了
- 先用postman进行测试,twitter采用OAuth1.0
Consumer Key 和 Consumer Secret 去管理平台获取
Access Token 和 Token Secret 客户端授权获得
Signature Method 固定值 HMAC-SHA1
Timestamp 时间搓
Nonce 随机数
Version 固定1.0
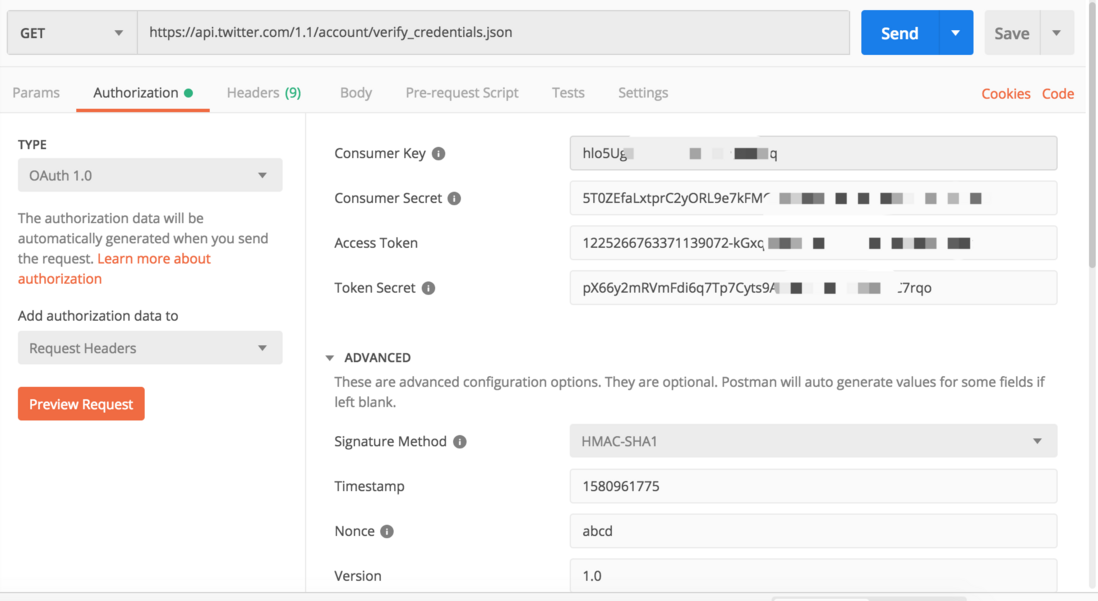
- 前面只是测试阶段配置是否正确,下面贴PHP代码:
<?php
//Twitter配置,管理后台查
$consumerKey    = '';
$consumerSecret = '';

//加密算法,自己百度回来的,
function get_signature($str, $key){
    $signature = "";
    if (function_exists('hash_hmac')){
        return base64_encode(hash_hmac("sha1", $str, $key, true));
    } else {
    //这里不解释,如果不支持,自己百度了
    }
    return $signature;
}


$time = time();
$oauth_consumer_key = $consumerKey;
$oauth_nonce= time() . rand();
$oauth_signature_method="HMAC-SHA1";
$oauth_timestamp=$time;
$oauth_version="1.0";
//请求方法,必需全部大写。
$httpMethod = 'GET';


//客户端获取的两个值
$input_token = "";
$input_token_sec = "";

//url,必需全部小写
$url = 'https://api.twitter.com/1.1/account/verify_credentials.json';

$params = [
    'oauth_consumer_key' => $oauth_consumer_key,
    'oauth_nonce' => $oauth_nonce,
    'oauth_signature_method' => $oauth_signature_method,
    'oauth_timestamp' => $oauth_timestamp,
    'oauth_version' => $oauth_version,
    'oauth_token' => $input_token
];

ksort($params);
$params = http_build_query($params);
//参数,此次请求中的除了oauth_signature以外的所有参数按照字母顺序升序排列,如果参数名相同,那么按照参数值的字母顺序升序排列。
// $params = "oauth_consumer_key={$oauth_consumer_key}&oauth_nonce={$oauth_nonce}&oauth_signature_method={$oauth_signature_method}&oauth_timestamp={$oauth_timestamp}&oauth_version={$oauth_version}";

//签名串(text)的构成:HttpMethod&url&参数。(一定是先各自urlencode后再用‘&’相连起来)
$signature_text = urlencode($httpMethod) . '&' . urlencode($url) . '&' . urlencode($params);

//oauth_consumer_secret&oauth_token_secret
$key = $consumerSecret . '&' . $input_token_sec;

$oauth_signature = get_signature($signature_text, $key);
// echo $oauth_signature . '<p>';

$oauth_signature = urlencode($oauth_signature);
//echo $oauth_signature . "</p>";

$httpHeader = [
    'Authorization: OAuth ' .
    'oauth_consumer_key='.$oauth_consumer_key .
    ',oauth_token='. $input_token.
    ',oauth_signature_method='.$oauth_signature_method .
    ',oauth_timestamp='.$oauth_timestamp .
    ',oauth_nonce='. $oauth_nonce .
    ',oauth_version='.$oauth_version .
    ',oauth_signature='.$oauth_signature
];

// echo $httpHeader[0];

$ch = curl_init();
curl_setopt($ch, CURLOPT_URL, $url);
curl_setopt($ch, CURLOPT_POST, 0);
curl_setopt($ch, CURLOPT_HTTPHEADER, $httpHeader);
curl_setopt($ch, CURLOPT_SSL_VERIFYPEER,false);
curl_setopt($ch, CURLOPT_HEADER, 0);
curl_setopt($ch, CURLOPT_TIMEOUT, 30);
curl_setopt($ch, CURLOPT_RETURNTRANSFER, true);

//自己设置代理
curl_setopt($ch, CURLOPT_HTTPPROXYTUNNEL, true);
curl_setopt($ch, CURLOPT_HTTPAUTH, CURLAUTH_BASIC);
curl_setopt($ch, CURLOPT_PROXYTYPE, CURLPROXY_HTTP);
curl_setopt($ch, CURLOPT_PROXY, '127.0.0.1');
curl_setopt($ch, CURLOPT_PROXYPORT, 1087);
$ret = curl_exec($ch);
if (false === $ret) {
    $ret =  curl_errno($ch);
}
curl_close($ch);
echo $ret;
评论
登录后参与技术讨论,分享你的经验与见解。
登录 / 注册暂无评论