Roundcube Webmail信息泄露漏洞(CVE

文章目录
Preface
Software: https://roundcube.net/
Versions: 1.1.x<1.1.2(亲测1.1.5也有效)
CVE: CVE-2015-5383
Author: adprotas
Release date: 2015-5-5
Reference
环境搭建
请参考:CentOS6 安装Sendmail + Dovecot + Roundcubemail
漏洞复现
本地环境:CentOS 6 + Roundcube 1.1.1
Roundcube Webmail 1.1.x before 1.1.2 allows remote attackers to obtain sensitive information by reading files in the (1) config, (2) temp, or (3) logs directory.

Roundcube Webmail 1.1.x before 1.1.2可以读取到config、temp、logs中的敏感信息,不需要账号密码
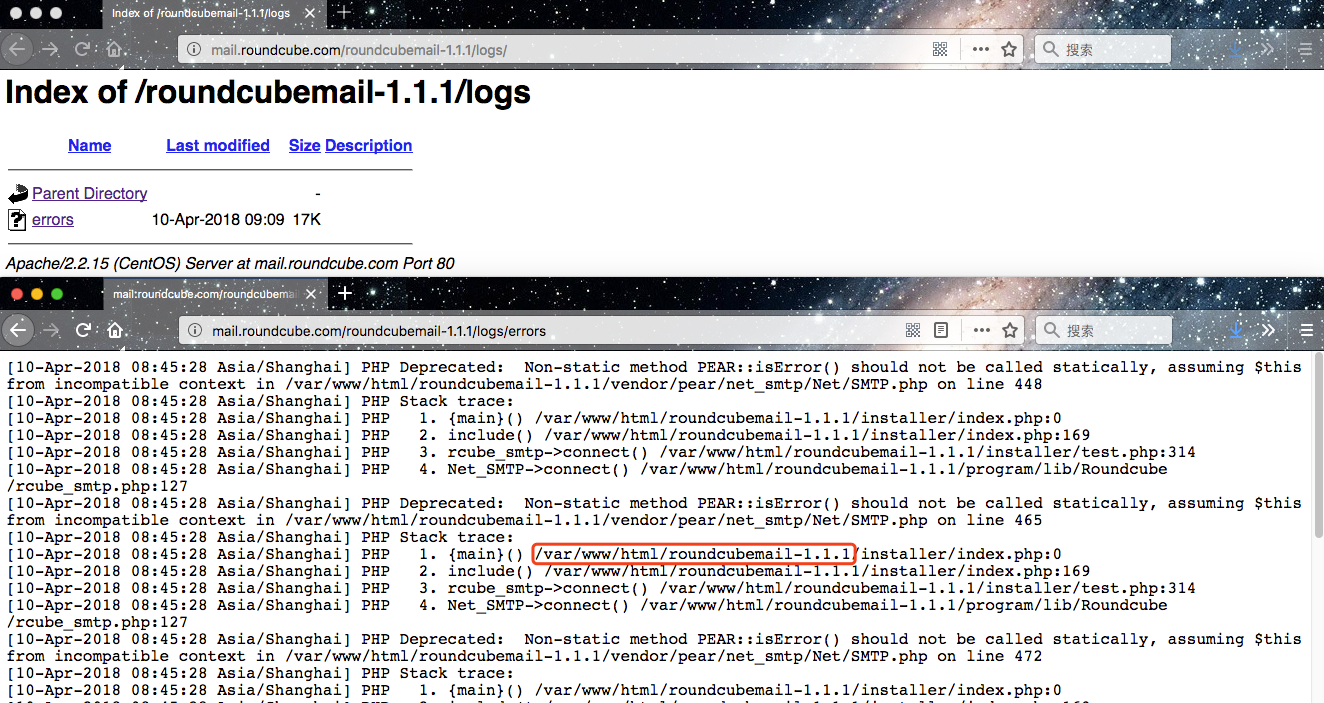
至少可以读取到Webmail路径信息,甚至可以读取到其他用户的session_id,进行登录操作。
评论
登录后参与技术讨论,分享你的经验与见解。
登录 / 注册暂无评论